AI Security
An operating model and reference architecture for deploying AI in regulated companies: risk tiers, embedded SDLC controls, and an authorization layer for agents, tools, data and models.
NIST AI RMF · EU AI Act · SOC 2 · ISO 27001Adam Fiejdasz · AI security and architecture · West Linn, Oregon
Security architect at a financial institution by day. Builder the rest of the time. I design the controls, identity and data architecture that let regulated companies put generative AI into production, and I ship the products to show it can be done.
CISM · AAISM · AWS Bedrock, SageMaker, CDK · 20+ years from change management to solution architecture
Most AI programs stall between the demo and the audit. The model works, then security, legal and risk ask how it is governed, who the agent is acting as, and where the data went. Nobody has an answer that fits in a control framework.
That gap is where I work. I have more than twenty years in technology: corporate communications and organizational change first, then global project management, business analysis and solution architecture, much of it in security. The last three I have spent applying that to AI: threat models for agents, guardrails on Bedrock, audit trails a regulator can read.
I also build. The software on this page I designed and built myself, with AI agents doing most of the typing. The architecture decisions are mine.
Each one has a problem, an architecture and a result.

An operating model and reference architecture for deploying AI in regulated companies: risk tiers, embedded SDLC controls, and an authorization layer for agents, tools, data and models.
NIST AI RMF · EU AI Act · SOC 2 · ISO 27001
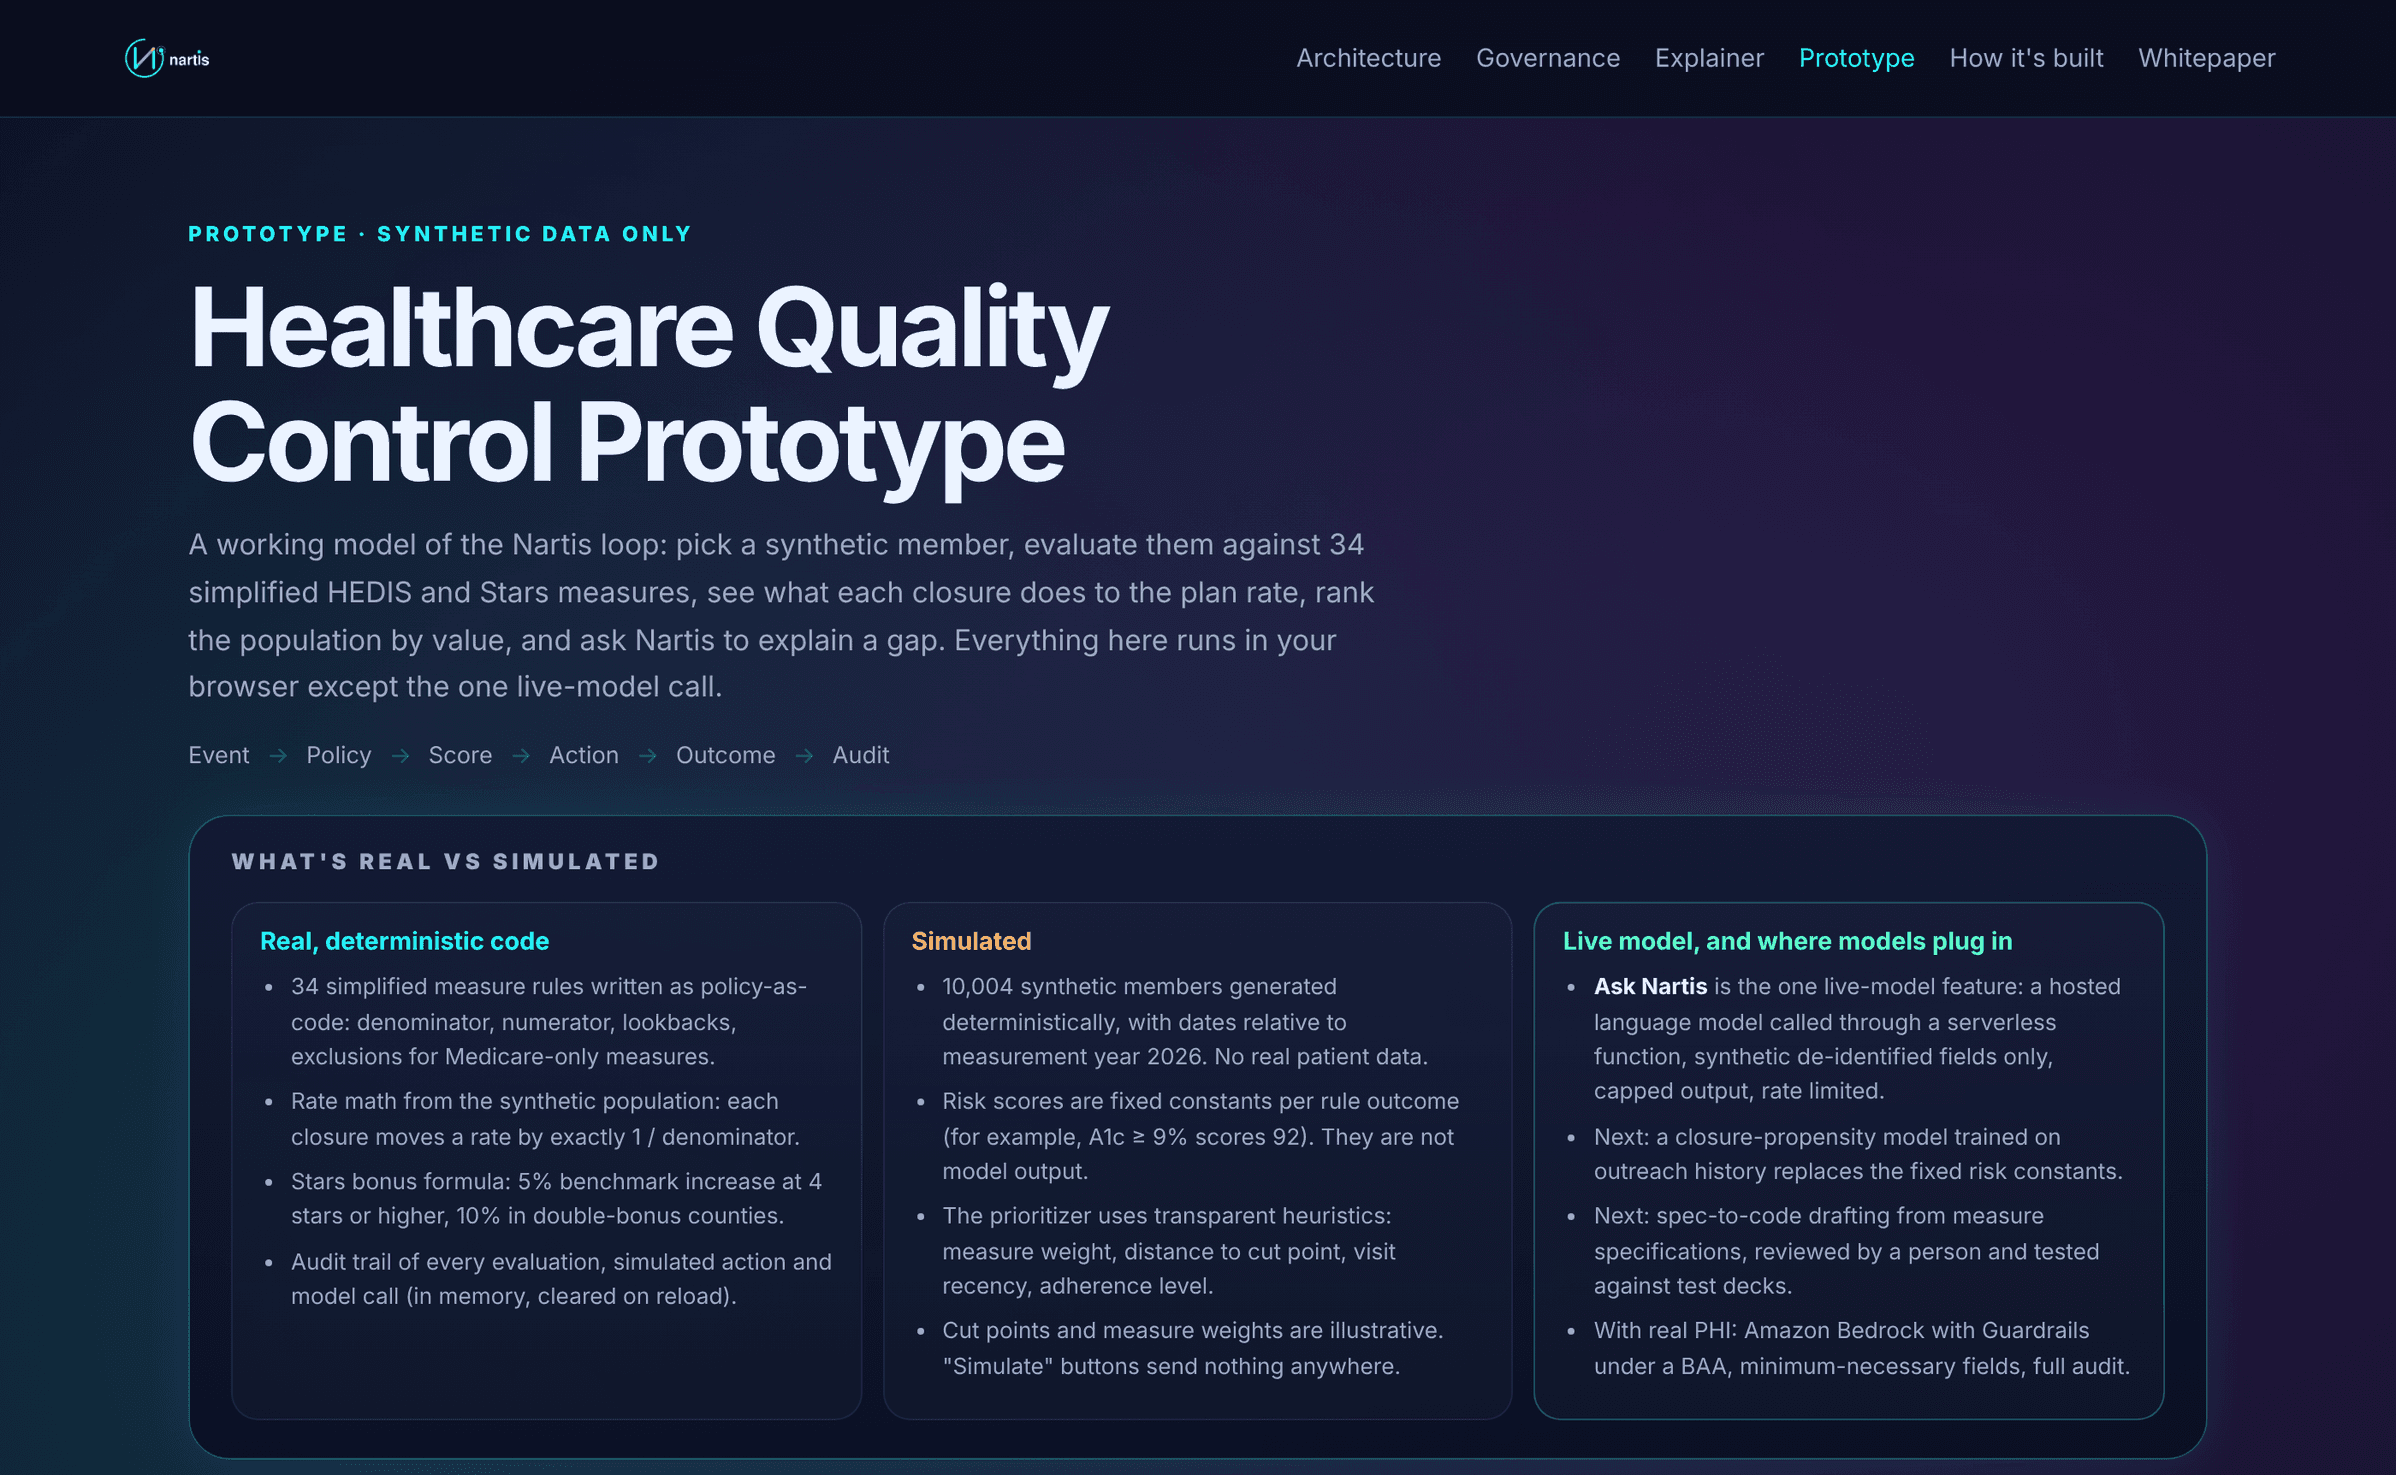
An AI-native platform for HEDIS and CMS Star Ratings: clinical data into a governed warehouse, measure logic that is transparent and auditable, results that quality leaders can act on. Designed and prototyped.
Designed and prototyped
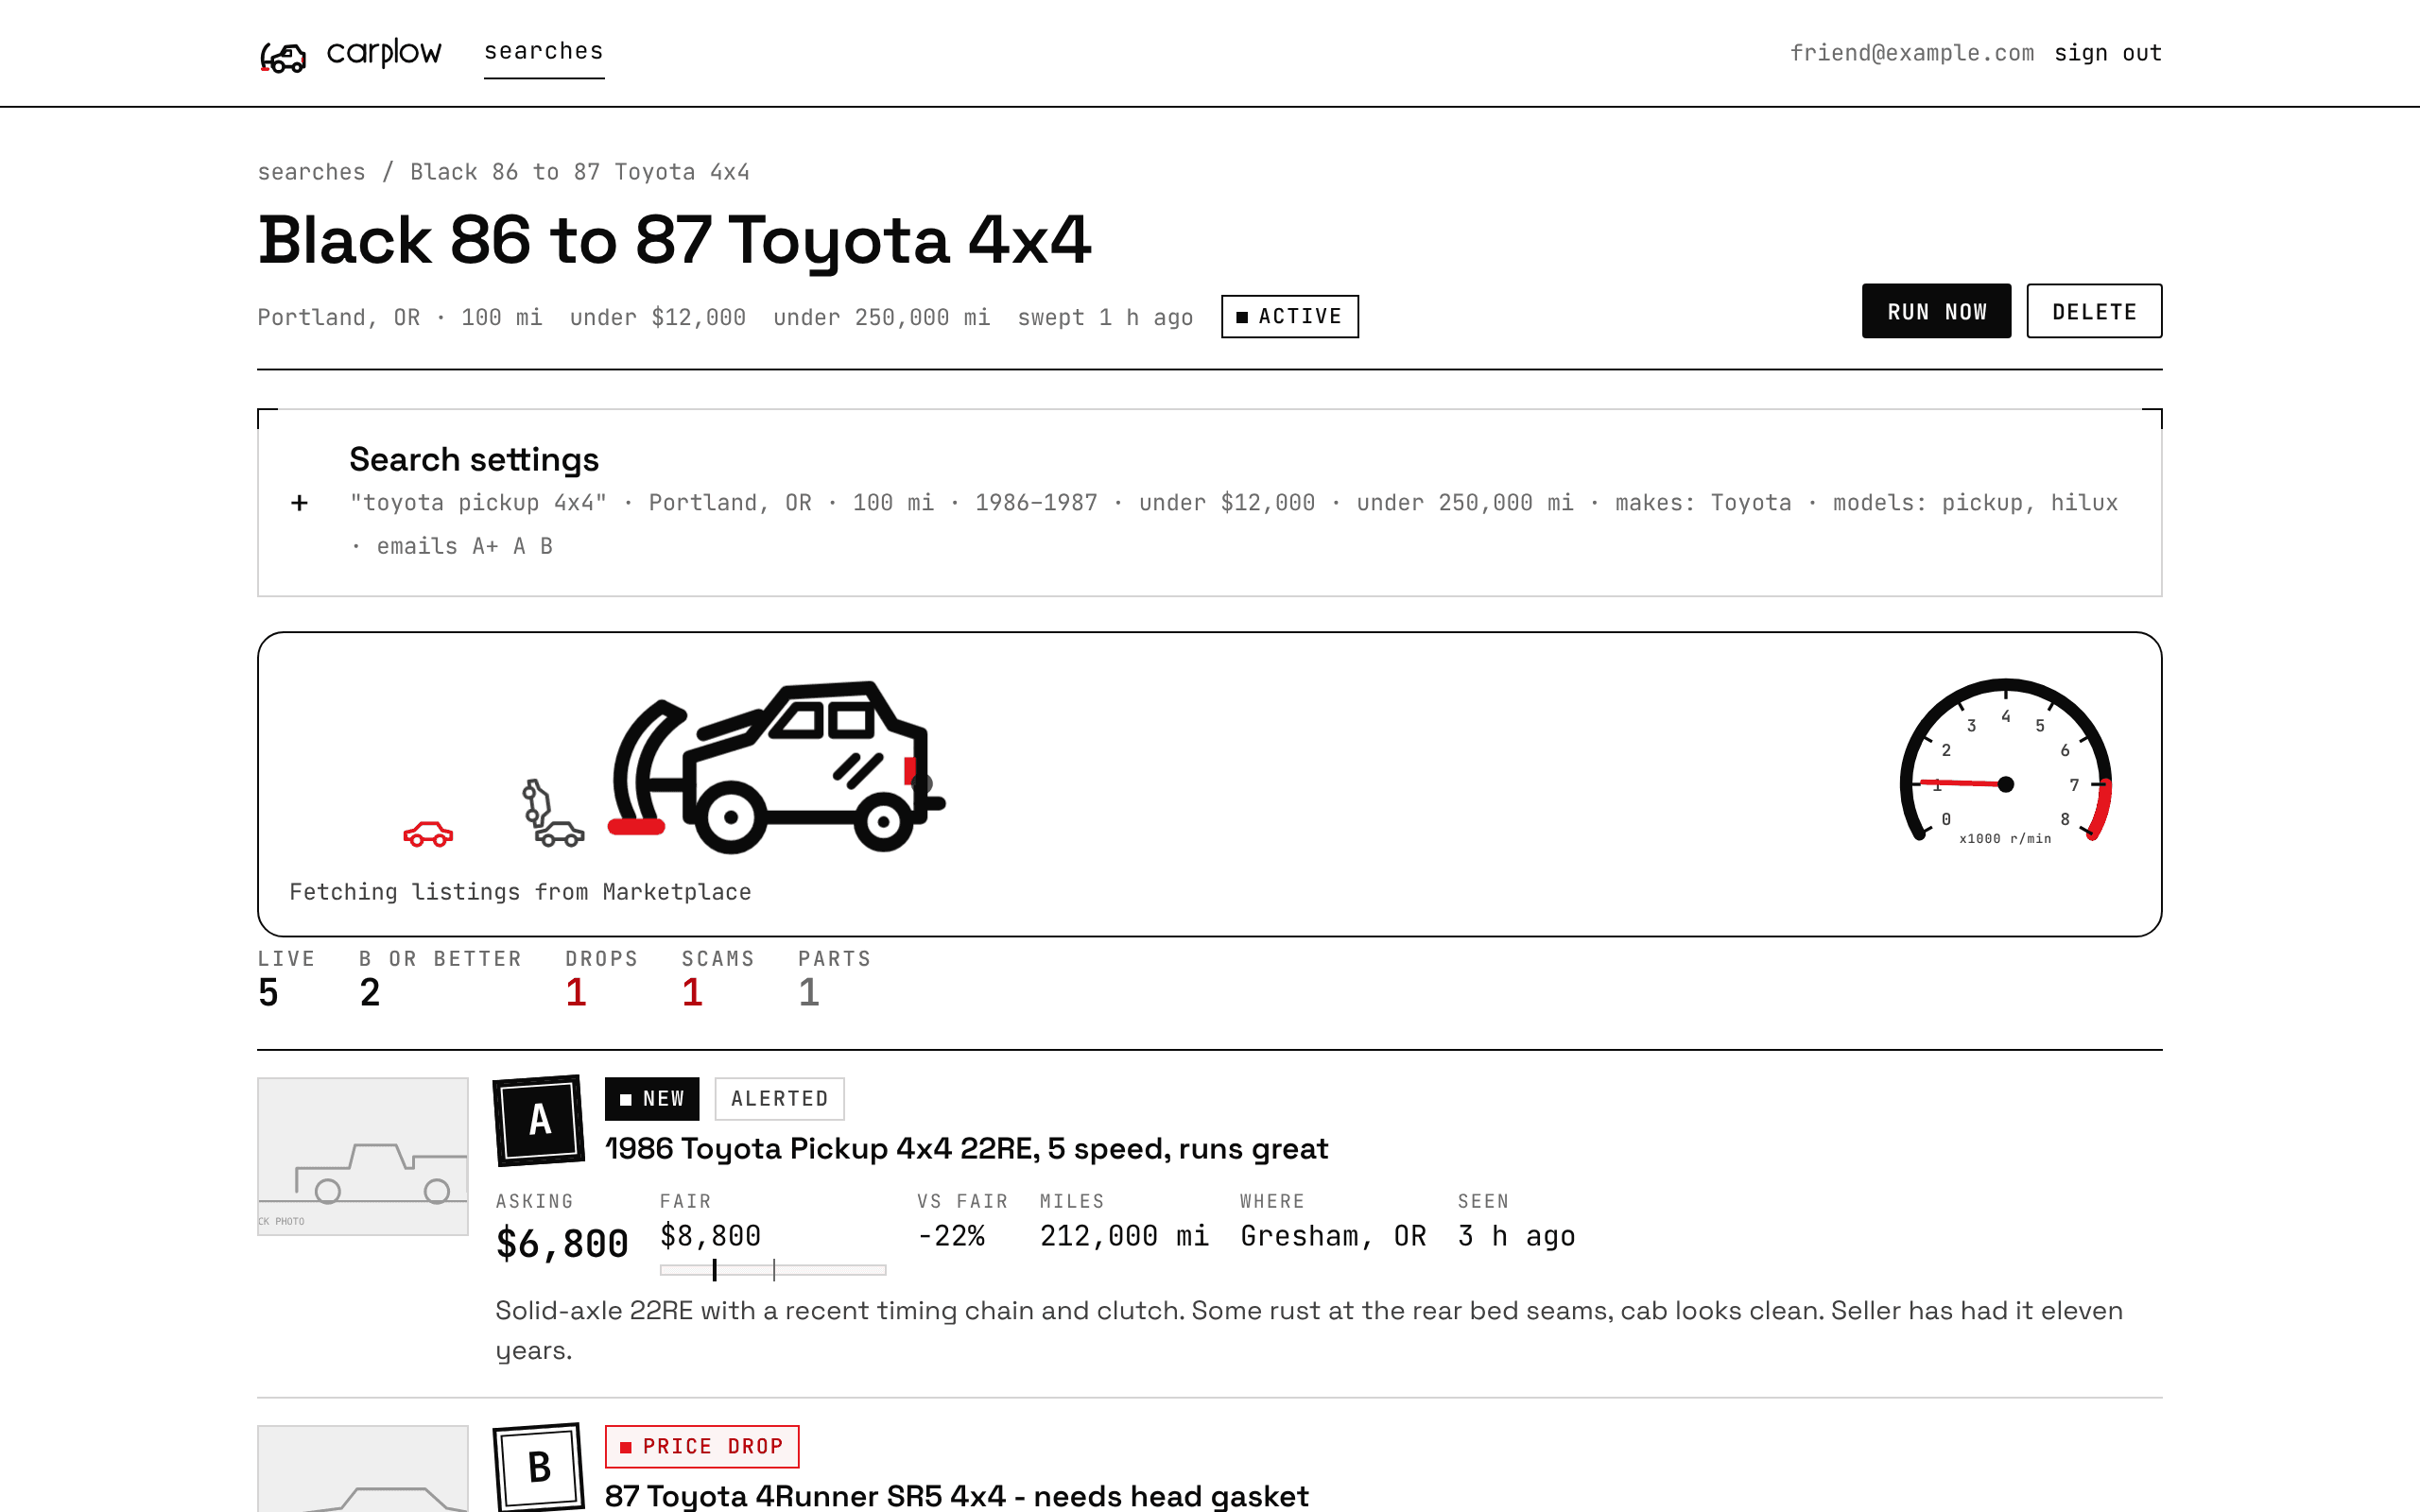
Watches Facebook Marketplace for each saved search, grades every listing with Claude against market value, and emails the grades you pick. Live for a small group of friends: Next.js on Vercel, AWS CDK back end.
Live · friends only · AWS CDK
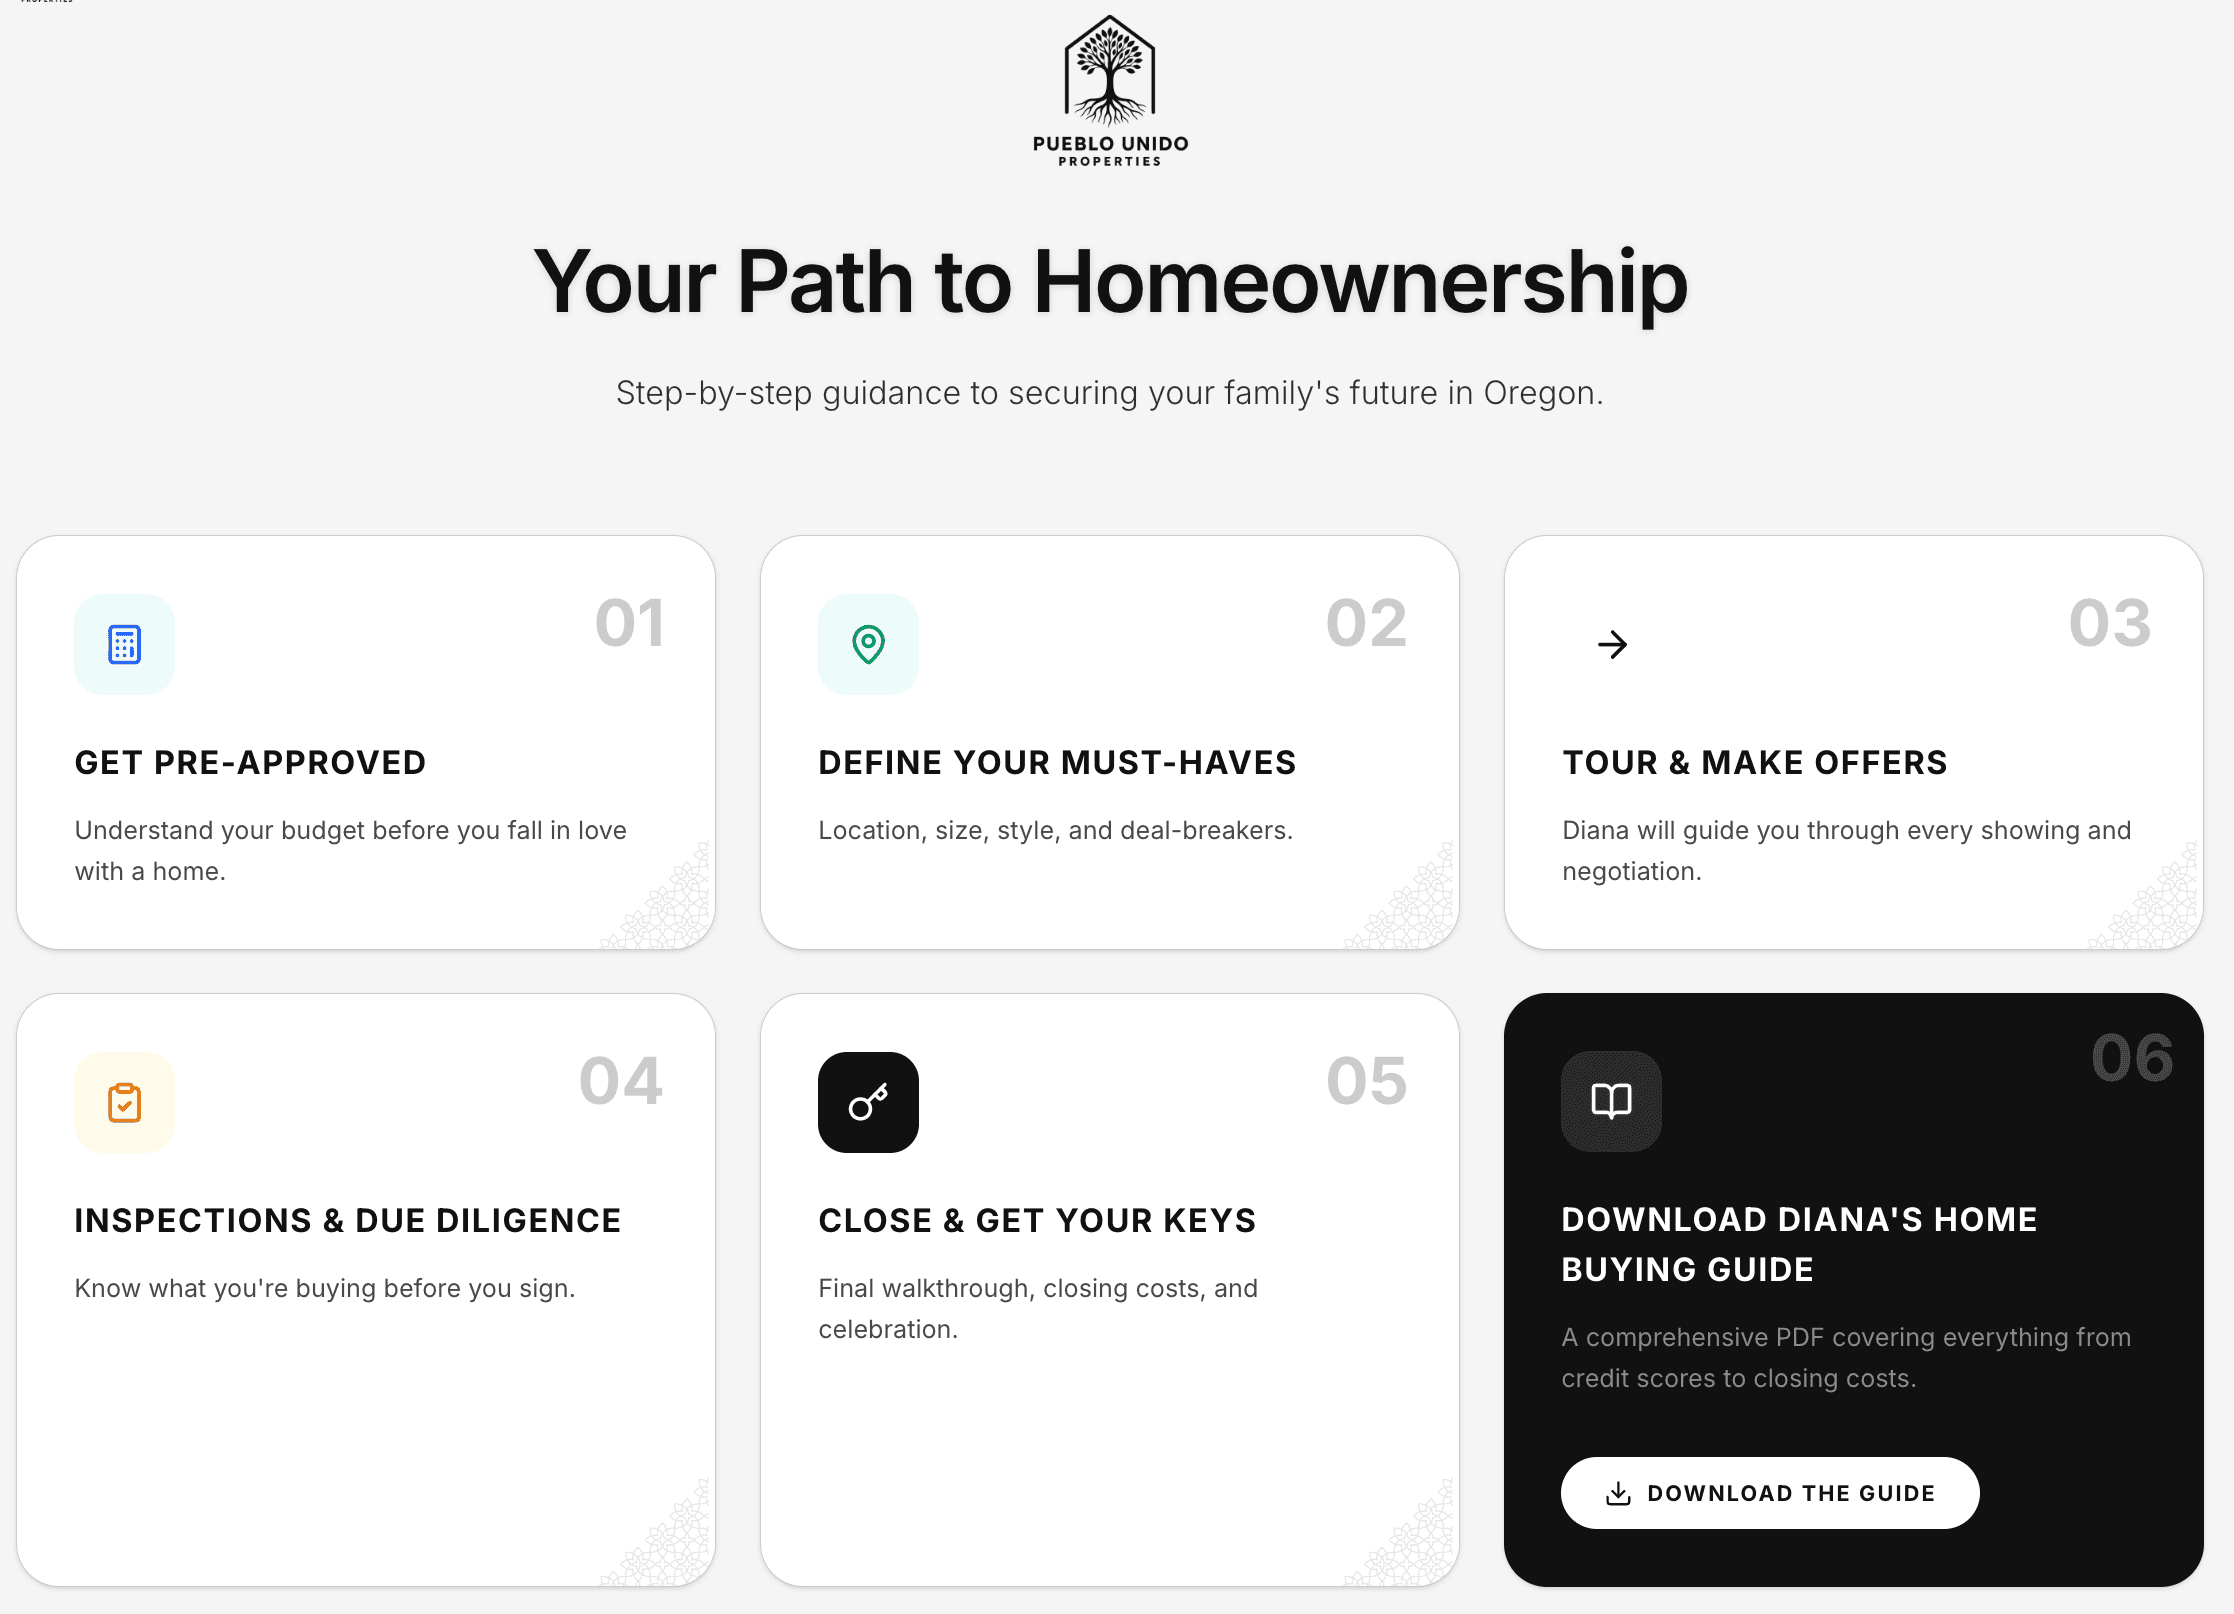
A listings site and an AI agent that answers buyers in English and Spanish, qualifies leads, books viewings and hands off to Diana, the agent, when a person adds value. Live for a working brokerage.
Live · pueblounidoproperties.comBusinesses, products and brand work. Different muscles, same process.
Oregon's first racing and flight simulator lounge, open in West Linn since August 2025. The marketing stack is AI-built: SEO, analytics, a nightly Mailchimp sync and a live lap-time leaderboard.
Open · West Linn, ORGames you play on a rowing machine: race a glowing ghost of your best row across a 3D lake, hop lily pads with stroke power, battle bosses that call interval challenges, row a Viking longship to a drummer's beat, outrow a horde through a flooded city, fly a cave shooter, or gallop a unicorn through the clouds. The rower's own tablet runs them with nothing else attached.
Live · rowplay.netA habit tracker where every check-in lays a stone. A week of habits becomes a course, courses raise a ziggurat, and everything you finish takes a plot in a city that never resets.
Preview · ziggurat.atomfade.comFive wordmarks and ten building directions for a Korean teriyaki drive-thru, delivered as an interactive review tool so the client could choose brand and architecture independently.
Concept · Phase 1 deliveredA browser-based 3D configurator: pick a bike, set every finish from plastics to spoke nipples, lay out graphics panel by panel, then save and share the build.
Live · motofig.comEngineering studies as interactive 3D models. Current entry: a rooftop hydroponic garden that lowers to harvest height on demand.
Study · garden.atomfade.comAgents write most of the code. I own the architecture, the security model and the decision log.
Risk tier, data classification, who the system acts as, what a bad day looks like. This is written before any code.
Diagrams, trust boundaries, identity for every agent and tool, logging that an auditor can follow. On AWS this is usually Bedrock with Guardrails, CDK, and CloudWatch.
Claude Code and friends do the typing. I set the plan, read every diff that touches auth, data or money, and keep a written record of each decision.
Everything I run has a live status page and a weekly review. If it is not measured it is not done.
Two to four weeks. You get a risk-tiered operating model, a gap list against NIST AI RMF and the EU AI Act, and a control set your engineers can live with.
Scoping, delegation and audit for agents that call tools and touch data. Reference architecture on AWS, policy model, secure RAG.
Four to eight weeks from brief to a running system on your cloud, with the architecture and decision log to take it to production.
I am a Senior Security Architect at a financial institution, focused on AI security and governance. Before that: enterprise risk and identity governance at Nike, and AI governance across a portfolio of early-stage ventures. I hold CISM and AAISM. Outside work I co-own Kartcade and I build things like the ones above. I live in West Linn, Oregon.